Who Holds the Keys? Preparing for the Day Your IT Supplier Cannot Answer
Photo: LLHZ2805, CC BY-SA 4.0, via Wikimedia Commons
The call that does not get returned
It seldom arrives as bad news. There is no formal notice, no administrator appointed, no email announcing the end. Instead, a ticket sits unacknowledged for a day, then two. The account manager's mobile goes to voicemail and the voicemail box is full. An invoice arrives from an unfamiliar trading name. Somebody in the office mentions that the person who used to handle their account has moved on, and that the new contact is, quote, getting up to speed.
For most UK SMEs the IT provider is a small business itself — often fewer than twenty people, frequently dependent on a handful of key individuals. That is not a criticism of the sector; it is a description of it. The consequence is that the concentration risk sits unexamined until the moment it matters, and the moment it matters is usually the moment when something has already broken.
The question worth asking this quarter is not whether a supplier might fail. It is whether, on the morning it does, your business could keep working without them and take control of its own systems within days rather than months.
What fails first, and in what order
In practice, the sequence is predictable — and it is governed by access control rather than by hardware.
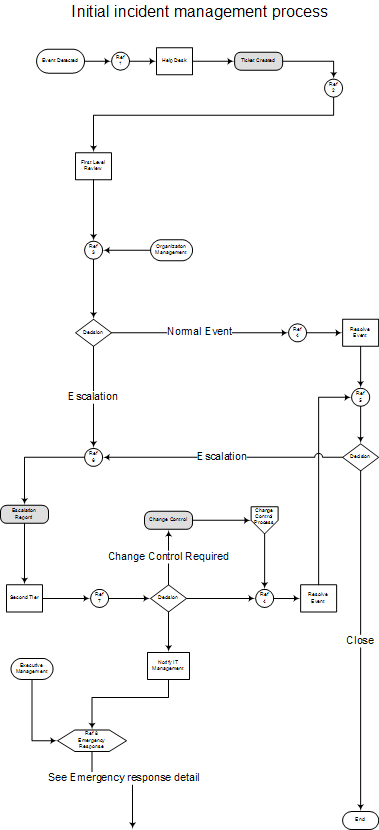
Email routing and the domain. If the domain is registered in the supplier's name, or the registrar account is theirs, you have no unilateral ability to change DNS records. That means no ability to repoint mail, no ability to move to a new provider, and a real possibility of an outage you cannot fix.
Administrator rights. Global Administrator on the Microsoft 365 or Google tenant is the whole business in one credential. Where that credential sits with a named individual at a third party, and no break-glass account exists in your own custody, you are a guest in your own tenancy.
The licence tenancy. Licences bought through a partner under a Cloud Solution Provider arrangement are attached to that partner's relationship. They can be transferred, but the transfer requires cooperation — precisely the resource that has just become unavailable.
Documentation and the asset register. Firewall rules, switch configurations, line-of-business application credentials, backup encryption keys, support contracts for hardware nobody remembers buying. All of it typically resides in a technician's notes or a password vault to which you have no administrative access.
Then, and only then, the operational gap. The absence of a person who knows how the estate is wired.
The clauses worth reading this month
Four contractual points repay attention now, while the relationship is healthy and the supplier is motivated to appear reasonable.
First, assignment and change of control. If the provider is acquired, does the contract transfer automatically, and do you retain a right to terminate without penalty within a defined window? Without that clause, you inherit a stranger.
Second, return of credentials and data. Insist on a specific obligation to hand over all administrative access, documentation and configuration records within a stated number of working days, in a stated format, following termination or insolvency. Vague promises of cooperation are worth little.
Third, exit assistance. Ask for a defined period of paid transition support at agreed rates — commonly thirty to ninety days — during which the outgoing provider must assist a successor. This is the clause that most often converts a crisis into an inconvenience.
Fourth, subcontractor disclosure. If parts of the service are delivered by a third party, you should know who they are, because their continuity matters as much as your supplier's.
Alongside these sit two practical safeguards. Put the domain in an account you own, paid for on your own card, with the registrar details in your name. And require that a break-glass administrator account exists in the tenant, credentials held by you in a sealed record with multi-factor authentication enrolled, tested on a schedule rather than assumed.
A one-page continuity checklist
This is the document to hold internally, reviewed twice a year and held offline as well as in the cloud.
- Domain registrar — account owner, login recovery route, expiry date, payment method.
- DNS — who controls the zone, where the records are documented, current export saved.
- Tenant — global administrator identities, break-glass account location, MFA method, date last tested.
- Licences — agreement type (direct or via partner), renewal date, notice period, transfer route.
- Data — backup platform, encryption keys, restore procedure, last successful test date.
- Credentials — where the vault lives, who can open it, business continuity contact for the platform.
- Asset register — hardware, serial numbers, warranty and support contract references.
- Named successor — one alternative provider briefed on the environment, or at minimum an identified technical contact.
- Communications plan — who tells staff, and where the fallback contact details sit if email itself is affected.
- Legal route — solicitor contact, notice template, director accountable for invoking it.
Ten lines. An afternoon to compile the first time, and perhaps an hour a year thereafter.
Reading the warning signs
Continuity planning is not disloyalty. Providers that are managed well do not object to a client knowing where its own domain is registered; the request is a reasonable one, and the response to it is informative either way.
What should prompt a review sooner rather than later: repeated changes of account manager, invoices arriving from a different legal entity, senior technical staff leaving in quick succession, refusal or delay when you ask for administrative access to your own tenant, security tooling lapsing without explanation, or renewals that are chased later each year. Individually, each is a nuisance. Together, they are a pattern.
The objective is not to prepare for the worst so much as to make the worst survivable. A business that owns its domain, controls its tenant, holds tested credentials and can name a successor is one that can absorb a supplier failure in a fortnight. A business that cannot do those things is one bad phone call away from a quarter it will spend explaining to clients why the email bounced.